Business Security
Verification Network

See who's verified. See who's vulnerable.
Report breaches confidentially.

New here? Start with Status Board to see who's verified, or This Week's Threats for the latest intelligence.

πŸ“‹ The Standard

8 Compliance Audit Checklist

How It Works

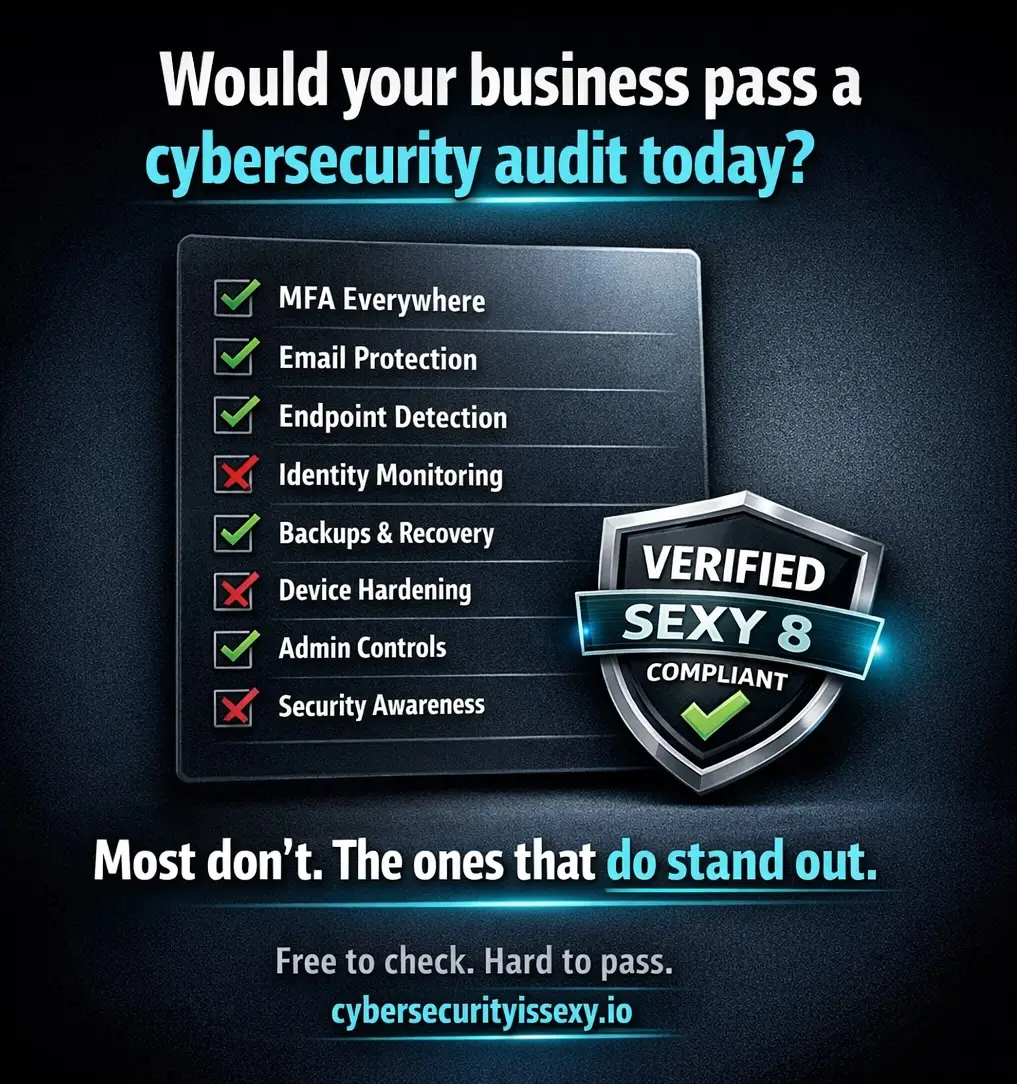
Businesses on our Status Board are measured against The Standard β€” 8 core security controls that prevent most cyber attacks.

Why "sexy"? Security is usually framed as a cost or checkbox. We call it "sexy" because when it's done right, it becomes a trust signal, competitive edge, and growth driver β€” not just protection. Businesses with strong security win deals, command premium pricing, and avoid the reputational devastation of a breach. It's not about fear; it's about aspiration.

πŸ“Š

Monitor the Board

See which local businesses are currently verified and their compliance status.

βœ…

Verify Your Business

Complete the audit checklist to see if you qualify for the badge.

πŸ›‘οΈ

Stay Protected

Get the weekly threat brief to stay ahead of active exploits and ransomware.

⚑

Operational Responsiveness

Security and operational readiness go hand-in-hand. Test and benchmark your inbound customer response speed on Response Radar β†’

View Status Board β†’ Get My Badge β†’

Why This Matters

Cybersecurity isn't just ITβ€”it's about trust, reputation, SEO, and business survival.

πŸ”’

Data Breaches Are Rising

60% of small businesses close within 6 months of a cyber attack. Basic security can prevent most incidents.
Source: Cybersecurity Ventures

🌐

Dark Web Exposure

Over 24 billion stolen credentials are traded on the dark web. Proper controls reduce your attack surface significantly.
Source: Forbes / Digital Shadows

🀝

Consumer Trust

87% of consumers will take their business elsewhere if they don't trust a company to handle their data responsibly.
Source: McKinsey & Company

πŸ“ˆ

SEO & Google Ranking

Google uses HTTPS/Security as a ranking signal. Verified listings build "E-E-A-T" (Trust) for local SEO.
Source: Google Search Central

πŸ’°

Insurance Savings

Proper security controls (like MFA) can lower cyber insurance premiums by up to 25-50% or make you eligible for coverage.
Source: Marsh / Global Insurance

βœ…

Responsiveness Matters

The FTC requires businesses to respond promptly to security risks. Silence is often viewed as negligence by regulators.
Source: FTC Security Guide

πŸ’Έ THE MATH OF FAILURE

Prevention vs. Catastrophe

⚠️ RESULTS ARE IN
Victim The Fatal Flaw The Prevention Tool The ROI Gap
πŸŽ“
Lincoln College
Closed (157 yr legacy)
No offline backups. Ransomware encrypted everything instantly.
βœ“ Immutable Cloud Backups
~ $500 / month
~ $6,000/yr
$50M+ LOST | $6K PREVENTED
βœ“ Prevention cost < 0.01% of loss
🚚
Small Carriers
Liquidated fleets
Weak passwords + No MFA enabled.
βœ“ MFA (Multi-Factor Auth)
$0 (Free Setting)
5 minutes to enable
BUSINESS COLLAPSE | $0
βœ“ Prevention cost < 0.01% of loss
πŸ₯
Petersen Health
Chapter 11 Bankruptcy
Unpatched remote access server (Citrix). Known bug left open.
βœ“ Auto-Patching Software
~ $3 - $5 / device
~ $500/mo
$40M FROZEN | $500/mo
βœ“ Prevention cost < 0.01% of loss
🚨 THE TAKEAWAY

Cyber defense isn't expensive. Recovery is impossible.
A verified business proves they have spent the pennies to save the millions.

βœ“ Prevention cost is negligible
βœ“ Recovery is financially impossible
βœ“ Verification = Security

Why We Started This

We built this project after watching too many preventable breaches unfold the same way: known security basics were ignored, warnings were delayed, and customers, employees, and partners paid the price. The pattern was consistent across industries and company sizes.

Our goal is straightforward: make cybersecurity expectations visible, measurable, and understandable before an incident happens. When a business strengthens core controls early, everyone connected to that business is safer.

A Short History

This verification directory began as a practical response to repeated owner-negligence scenarios and avoidable incidents seen in day-to-day advisory work. Instead of waiting for another post-breach cleanup, we published a clear baseline and made status public so business owners can act sooner.

We continue to refine the methodology using current breach trends and operational lessons from remediation engagements, but the core principle has not changed: prevention is almost always less costly than recovery.

Our Position

Breach statistics consistently show that investing in foundational controls is materially more effective than relying on post-incident recovery. This site exists to make that reality harder to ignore.

How Our Business Verification Works

A transparent process to separate the security leaders from the talkers.

1

Invite

Businesses may appear here through direct outreach, routine screening, professional contact, or third-party submissions. Verification is available voluntarily, but listings are not limited to businesses that received a formal invitation.

2

Assess

We evaluate their security controls against our published baseline criteria.

3

Remediate

Businesses must remediate identified gaps or accept a failed / at-risk outcome if they ignore critical issues or refuse to engage.

4

Publish

We publish the verification status transparently for consumers and partners.

Our Business Verification Methodology

Participation in our verification program is voluntary. Passing it is not. If a business ignores documented outreach, refuses to answer basic verification questions, or dismisses credible security concerns, that alone fails verification for trust and governance reasons.

Automatic Failure and Escalation Triggers

We do not consider negligence to be a neutral outcome. A business can fail verification or be escalated to a public at-risk label when the pattern shows it was warned and chose not to engage.

  • Documented notice of critical vulnerabilities or exposed systems followed by dismissal, delay, or no meaningful remediation plan.
  • Ignoring security-related outreach that contains evidence of a real issue, a required action, or a reasonable opportunity to correct the problem.
  • Refusing to answer basic verification questions or provide a reasonable response about baseline protections after being given a fair opportunity to do so.
  • Leadership or decision-makers openly minimizing cybersecurity risk, treating basic controls as optional, or refusing to address known business-email-compromise exposure.
Security Culture and Leadership Posture (Behavioral Risk Indicator)

Technical controls are only part of the risk picture. A business's willingness to engage with documented security concerns is itself a meaningful signal. If a business is given credible findings or straightforward verification questions and chooses silence, dismissal, or avoidance, we treat that as a governance problem, not an administrative miss.

What this does NOT mean: Non-response is not proof of compromise. It is, however, enough to fail verification because trust requires transparency and a willingness to engage on basic security questions.

Bottom line: If a business is told about a credible security concern or asked basic verification questions and chooses not to respond, that business fails verification on trust grounds.

The "Sexy 8" Baseline Controls (Backed by Data):

  • 1. MFA on Critical Systems: Multi-factor authentication enforced on email (M365/Google Workspace) and remote access (VPN/RDP). Third-party SaaS MFA is recommended but not required for baseline verification.
    CISA Data: MFA dramatically reduces account takeover risk on the most targeted entry points.
  • 2. Device Encryption: Full-disk encryption (BitLocker/FileVault) on all computers.
    FTC Requirement: Essential for Safe Harbor if devices are lost/stolen.
  • 3. Cloud-Integrated Backups: Email and cloud storage (M365/Google Drive) are backed up through a third-party backup platform. Local-only data not synced to cloud storage requires separate backup coverage.
    Ransomware Defense: Recoverable backups remain the most important control for operational recovery.
  • 4. Next-Gen Defense: EDR/MDR protection (not just free antivirus).
    Industry Standard: Legacy AV misses 60% of modern malware.
  • 5. Email Security - At Least for Key Users: Anti-phishing and DLP/encryption protections for business-critical mailboxes (leadership, finance, HR, and privileged admins), plus SPF/DKIM/DMARC on the primary domain.
    Verizon DBIR: Email remains one of the most common initial access vectors in real-world breaches.
  • 6. Patching: Automated updates for OS and software within 30 days.
    CISA KEV: Hackers exploit known bugs within 15 days on average.
  • 7. Incident Response Plan: A documented breach response and recovery runbook maintained by the IT provider. Client acknowledgment is recommended but not required for baseline verification.
    NIST Framework: Respond and Recover capabilities materially reduce downtime and breach impact.
  • 8. Independent Security Oversight (No DIY): Security controls must be managed or independently validated by qualified IT/security professionals. Solely self-managed ("DIY") security does not qualify.
    NIST SP 800-53 (AC-5): Separation of duties reduces risk by requiring independent roles and oversight.  |  IBM Cost of a Data Breach: Longer detection/containment lifecycles and weaker governance materially increase breach impact.

Website Security Headers (Informational Bonus)

We scan each business's website using SecurityHeaders.com and note the grade on their verification listing. This check evaluates HTTP response headers that protect site visitors from common attacks.

Headers we look for:

  • Strict-Transport-Security (HSTS) β€” Forces HTTPS connections. Recommended: max-age=63072000; includeSubDomains
  • X-Frame-Options β€” Prevents clickjacking. Recommended: DENY
  • X-Content-Type-Options β€” Prevents MIME sniffing. Recommended: nosniff
  • Content-Security-Policy (CSP) β€” Controls resource loading. Recommended: default-src 'self'; form-action 'self'; object-src 'none'; frame-ancestors 'none'
  • Referrer-Policy β€” Controls referrer information. Recommended: strict-origin-when-cross-origin
  • Permissions-Policy β€” Restricts browser features. Recommended: disable camera, microphone, geolocation unless needed.

Important: This is an informational bonus, not a pass/fail requirement. Many small business websites built on Wix, Squarespace, or shared hosting cannot configure these headers without developer access. A low grade is noted on the listing but does not prevent Verified status.

Grading display on listing:

  • A+ / A β€” 🟒 Hardened
  • B / C β€” 🟑 Partial
  • D / E / F β€” πŸ”΄ Needs Improvement

Verification Labels

Verified - Managed: Active MSP-managed security controls are deployed and continuously monitored against the Sexy 8 baseline.

Verified - Validated: Meets the managed baseline and includes recent evidence checks against defined control thresholds.

Vulnerable: Baseline controls are not met, or verified evidence shows known weaknesses remain unresolved.

At-Risk - Non-Responsive: The business was contacted about verification or security concerns and failed to engage after documented attempts. This fails verification on transparency and trust grounds, even when it is not proof of compromise.

Note: "MFA" is measured on critical systems (email + remote access) for baseline verification. Broader SaaS MFA and full-mailbox coverage are encouraged and may be required for higher validation tiers.

Need help meeting these standards?
These controls are standard inclusion in "Worry-Free IT" plans from our partner, USTech.Ninja.

Important Note: Our ratings reflect our own criteria and professional judgment. They are not legal compliance determinations and should be considered one factor among many when evaluating a business's security posture.

Business Verification Status Board

Real transparency about which businesses take cybersecurity seriously.

Verified? Get your badge β†’ β€’ Audit team response speed on Response Radar β†’

Verified & Armored
Vulnerable
Business Name Location Industry Status Headers Last Verified
Channel Islands Mortgage β†— Ventura County, CA Mortgage Services Verified - Managed A+ Feb 2026
Channel Islands Law Ventura County, CA Legal Services Verified - Managed A+ Feb 2026
Reverse Mortgage Northwest Pacific Northwest Mortgage Services Verified - Managed A+ Feb 2026
OC Home Loans Orange County, CA Mortgage Services Verified - Managed A+ Feb 2026
Ellevate Insurance Arizona Insurance Verified - Managed A+ Feb 2026
Genrose Insurance β†— Scottsdale, AZ Insurance Agency Verified - Managed A+ Sep 2026
Lisa G Travel Arizona Travel Services Verified - Managed A+ Feb 2026
AZ Baum Plumbing β†— Arizona Home Services Verified - Managed A+ Feb 2026
Erik Kelly Group Arizona Real Estate Verified - Managed A+ Feb 2026
DustSharkz Tempe, AZ Service Business Verified - Managed A+ Feb 2026
OCA Greater Phoenix Chapter Scottsdale, AZ Non-Profit / Community Advocacy Verified - Managed A+ Sep 2026

Verification status reflects the published baseline and is updated as evidence and monitoring data are reviewed.

Business Name Location Industry Status Headers Reason
micro1 (micro1.ai) Remote / US-based AI / Talent Platform Vulnerable - Critical Risk N/A Advertises legitimate IT/tech jobs, funnels candidates into AI video interviews, and uses responses to train AI models with no real hire. Glassdoor flagged a "Dangerous scam - personal data theft warning" and public complaints note early requests for passport/government ID. Passive technical note: Google Workspace MX, SPF uses ~all, DMARC is p=none, and the web front is Cloudflare/Webflow with HSTS, XFO, and a basic CSP.
Crossing Hurdles Remote Recruiting / Talent Broker Vulnerable - Critical Risk N/A Front organization that funnels candidates into Mercor AI talent platform to collect referral fees. Public reporting cites fake high-salary listings, unpaid assessments, AI interviews, and bait-and-switch recruiting tactics. Passive technical note: Google Workspace MX, SPF includes Google/Mailgun/JobDiva, DMARC is p=none, and Netlify serves the site with HSTS, nosniff, referrer-policy, and permissions-policy.
Turing.com Palo Alto, CA AI / Talent Platform Vulnerable - High Risk N/A Farms engineers and IT talent for AI training tasks under the guise of traditional job titles, with applicants reporting the funnel shifts from IT roles into AI operations and training work. Passive technical note: Google Workspace MX, DMARC is p=quarantine, and the Imperva front has strong headers but a very broad CSP / third-party dependency surface.
Sibitalent Corp Remote / US-based recruiting IT Staffing / Recruiting Vulnerable - Critical Risk N/A Glassdoor review alleges the company asks candidates for government ID, SSN, and other sensitive documents, creating a direct identity-theft and impersonation risk for IT professionals. Passive technical note: O365 MX, DMARC is p=none, and the apex redirects to HTTP on www with only basic Apache response headers observed.
Mercor Remote / US-based AI Talent Platform Vulnerable - Critical Risk N/A Appears in a connected recruiting ecosystem with Crossing Hurdles, micro1, and Turing. Public LinkedIn posts describe it as a predatory AI-talent ecosystem with referral farming, ghosted pay, and AI interview data harvesting. Passive technical note: Google Workspace MX, DMARC is p=quarantine, and the web front is strongly hardened but very dependency-heavy with a broad CSP and many third-party services.
Lucey Accounting Arizona CPA / Accounting Services Vulnerable - High Risk F Direct self-reported cybersecurity limitations and no follow-up remediation confirmation.
Go Gilbert Gilbert, AZ Real Estate / Community Platform Vulnerable - High Risk F Contacted owner on Feb 23, 2026 regarding identified security concerns. No remediation or verification response received.
Scottsdale Living Scottsdale, AZ Real Estate / Community Platform Vulnerable - High Risk F Contacted owner on Feb 23, 2026 regarding identified security concerns. No remediation or verification response received.
Living North Phoenix North Phoenix, AZ Real Estate / Community Platform Vulnerable - Critical Risk F Contacted owner on Feb 23, 2026 regarding identified security concerns. No remediation or verification response received.
CH Winery Unknown Hospitality / Winery Vulnerable - Critical Risk F Client-reported subdomain login flow transmitting credentials in plaintext. Immediate remediation and encrypted transport enforcement required.
Rod & Panel β†— Scottsdale, AZ Home Design / Window Treatments Vulnerable - High Risk F Primary domain is missing DMARC and DKIM records. SPF is present with hard fail (-all), but outbound email remains easier to spoof until DMARC and DKIM are configured.
Rosemary Bookkeeping (Goska Dabrowski) β†— United Kingdom Bookkeeping Services Vulnerable - Critical Risk F Email authentication baseline failure: missing SPF and DMARC records; no common DKIM selectors were detected.
Soles For Jesus (Yenh Mikolajewski) β†— Wisconsin Non-Profit / Humanitarian Vulnerable - Critical Risk F Email authentication baseline failure: missing SPF and DMARC records; no common DKIM selectors were detected.
Desert Land Group (Mai Luke) Arizona Real Estate Development Vulnerable - High Risk F Email authentication baseline failure: missing SPF record and no common DKIM selectors were detected.
PXG (PARSONS XTREME GOLF) (Daniel Convery) Scottsdale, AZ Sports Equipment / Manufacturing Vulnerable - High Risk F Email authentication baseline failure: missing SPF record on the primary domain.
Panasonic Solutions for Business (Jeff Russomanno) Newark, NJ Technology / Electronics Vulnerable - Critical Risk F Email authentication baseline failure on the listed subdomain: missing SPF and DMARC records; no common DKIM selectors were detected.
Accent Building Restoration, Inc (Sugey Ostergaard) Phoenix, AZ Construction / Restoration Vulnerable - High Risk F Email authentication baseline failure: missing DMARC record.
My PC Techs Phoenix, AZ Technology Services Vulnerable - High Risk F Email authentication baseline failure: missing DMARC record.
Home Fur Good Phoenix, AZ Nonprofit / Animal Rescue Vulnerable - High Risk Not Scored Primary email-authentication gap observed on 2026-05-19: no DMARC record was returned for _dmarc.homefurgood.org. SPF is present and DKIM selectors responded, but the mixed Bluehost, Constant Contact, and Microsoft 365 sender footprint should be reviewed and tightened.
The Elyte Law Firm, PLLC Phoenix, AZ Legal Services / Criminal Defense Vulnerable - High Risk F Public website lists a consumer Gmail mailbox (`[email protected]`) as a primary client contact channel alongside firm-branded email, increasing intake confidentiality, account governance, and business-email-compromise exposure for a legal practice.
Journeys & Bridges Transitional Housing Phoenix, AZ Transitional Housing / Social Services Vulnerable - High Risk F Public-facing intake and contact workflows for a health-adjacent transitional housing provider rely on a consumer Gmail mailbox rather than a domain-managed business address, increasing confidentiality, governance, and business-email-compromise exposure for sensitive communications.
The Therapy Doctor PLLC Scottsdale, AZ Healthcare / Concierge Physical Therapy Vulnerable - High Risk F Passive baseline failure for a healthcare-adjacent practice: no DMARC record was returned for the primary domain, SPF remains in soft-fail mode (~all), and no common DKIM selectors were detected. Escalated further due to lack of communication and no verification response.
linqd. Gilbert, AZ Technology Vulnerable - Critical Risk F Email authentication baseline failure: missing DMARC record and no common DKIM selectors were detected.
DS Law AZ (Ahmed) Arizona Legal Services / Law Practice Vulnerable - High Risk F Passive baseline failure: missing DMARC record, no HSTS observed, and no Content-Security-Policy observed on the public website.
LocalFi (Kim) Arizona Marketing / Local SEO Vulnerable - High Risk F Passive baseline failure: listed domain redirects to localfiseo.com, missing DMARC record on the listed domain, and multiple common web security headers were not observed.
The Honey Foundation (Jaime) Arizona Non-Profit / Foundation Vulnerable - High Risk F Passive baseline failure: DMARC is present only in monitoring mode (p=none), and no common HSTS, CSP, X-Frame-Options, X-Content-Type-Options, or Referrer-Policy headers were observed.
helpful (Kirsten) Arizona Business Services Vulnerable - High Risk F Email authentication baseline failure: no DMARC record was found for the primary domain.
ACC Insurance Agency (Caleb Kemp) Arizona Insurance Agency Vulnerable - High Risk F Passive baseline failure: missing DMARC record, and no common HSTS, CSP, X-Frame-Options, X-Content-Type-Options, or Referrer-Policy headers were observed.
Priority Roofing (Jordan Robinson) Arizona Construction / Roofing Vulnerable - High Risk F Passive baseline failure: DMARC is present only in monitoring mode (p=none), and no common HSTS, CSP, X-Frame-Options, X-Content-Type-Options, or Referrer-Policy headers were observed.
Happy Light Company (Anthony Wilson) Arizona Home Services / Lighting Vulnerable - High Risk F Email authentication baseline issue: multiple SPF policy strings were observed in DNS TXT output, and DMARC is present only in monitoring mode (p=none).
Blackstone Roofing Group (Shaun Bures) Arizona Construction / Roofing Vulnerable - High Risk F Passive baseline failure: missing DMARC record, and no common HSTS, CSP, X-Frame-Options, X-Content-Type-Options, or Referrer-Policy headers were observed.
Oppty Unlimited United States Small Business Consulting / Sales Operations Vulnerable - High Risk F Passive baseline failure: DMARC is present only in monitoring mode (p=none), SPF remains soft fail (~all), and no common CSP, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, or Permissions-Policy headers were observed on the public website. Escalated further due to documented non-response after direct outreach and scheduled contact.
MNO Referrals United States Business Networking / Referral Organization Vulnerable - High Risk F Passive baseline failure: DMARC is present only in monitoring mode (p=none), HSTS is effectively disabled (max-age=0), and no common CSP, X-Frame-Options, Referrer-Policy, or Permissions-Policy headers were observed on the public website. Escalated further due to lack of communication and no verification response.
InsuranceProAZ (Bret Godsey) Arizona Insurance Agency Vulnerable - High Risk F Passive baseline failure: DMARC is present only in monitoring mode (p=none), DNS TXT output appears to mix authentication policy text, and no common web security headers were observed.
The Neely Group Phoenix, AZ Financial Services / Financial Planning Vulnerable - High Risk F Escalated due to documented security-culture and leadership-posture concerns after professional engagement, combined with email security posture concerns that materially increase business-email-compromise and client-trust risk.
Prestige Accounting Arizona CPA / Accounting Services Vulnerable - High Risk B Email security gaps: DMARC, DKIM missing; SPF soft-fail (~all), allowing trivial spoofing. Financial firm handling sensitive PII without basic email authentication poses a material BEC risk. Client portal (TaxDome) is segregated, but public communications remain unsecured.
Almeida Roofing Inc. Phoenix / Maricopa County, AZ Construction / Roofing Vulnerable - High Risk Not Scored Passive verification failure captured 2026-08-10: public business communications use a consumer Gmail mailbox ([email protected]), DMARC is present only in monitoring mode (p=none), and HSTS/CSP were not observed on the public HTTPS response. X-Frame-Options, X-XSS-Protection, and X-Content-Type-Options were observed. This is a public baseline finding, not evidence of compromise or unauthorized access.
Margie Mae's Holiday Decor (MM Holiday Decor) Arizona Holiday Lighting / Seasonal Decor Vulnerable - High Risk F Critical email security baseline failure: No SPF, no DMARC, and no DKIM in place β€” allowing trivial domain spoofing from any sender. For a business that processes vendor payments and has documented DLP leakage events involving bank routing information, the absence of basic email authentication creates a material business-email-compromise risk. Additionally, no common web security headers (CSP, XFO, HSTS) were observed on the public website. Active phishing pressure was independently confirmed during a security review window, and the Guardz baseline score of 59/100 further supports the vulnerable classification.
Precision Auto Body Tempe / Chandler, AZ Automotive / Collision Repair Vulnerable - High Risk F High local customer trust and strong collision repair standing, but critical technical baseline gap observed: missing SPF and DMARC records on primary domain, allowing trivial domain spoofing and business email impersonation.
Dirk's Electric Arizona Contracting / Electrical Services Vulnerable - High Risk F Master licensed electrical contractor with strong industry reputation; technical baseline gap observed: missing SPF and DMARC records on primary domain.
Hope for the Homeless Arizona Nonprofit / Community Outreach Vulnerable - High Risk F Grassroots community outreach nonprofit delivering essential aid; technical baseline gap observed: missing SPF and DMARC records on primary outreach domain.
RN Patient Advocates of Arizona Arizona Healthcare / Patient Advocacy Vulnerable - High Risk F Clinical patient advocacy handling sensitive health intake; missing DMARC record and SPF soft-fail (~all), exposing client medical and care coordination communications to spoofing risks.
Nicki Fit A to Z Scottsdale, AZ Health & Fitness Vulnerable - High Risk F Active local fitness and mobility brand; email authentication in monitor-only mode (p=none) with DMARC policy not actively enforcing domain protection.
Brewers AC & Heating, LLC Arizona HVAC & Mechanical Vulnerable - High Risk F Established family-owned HVAC contractor; email authentication baseline gap observed: missing DMARC record, leaving billing and quote communications exposed to spoofing.
South Mountain Auto Detail Phoenix, AZ Automotive Detailing Vulnerable - High Risk F Mobile auto detailing provider with strong local customer reputation; technical baseline gap observed: missing SPF and DMARC records on primary domain.
Interstate Auto Repair Arizona Automotive Mechanical Repair Vulnerable - High Risk F Longstanding automotive repair facility (member since 2017); technical baseline gap observed: missing DMARC record on primary domain.
EMG Barbershop Arizona Men's Grooming / Personal Care Vulnerable - High Risk F Concierge luxury grooming provider; technical baseline gap observed: missing SPF and DMARC records on primary client booking domain.
Signarama Chandler Chandler, AZ Commercial Signs & Branding Vulnerable - High Risk F Commercial signage and architectural branding provider with broad commercial client base; technical baseline gap observed: missing DMARC record on primary domain.
Ahwatukee Flowers Ahwatukee, AZ Florist / Retail & Events Vulnerable - High Risk F Premier local floral boutique with high community standing; email authentication in monitor-only mode (p=none) with broad third-party marketing sender footprint.
ARC Renovations and Construction Arizona General Contracting / Remodeling Vulnerable - High Risk F Licensed general contractor managing high-value residential renovations; technical baseline gap observed: missing DMARC record on primary domain.
Hayes Insurance & Financial Services Arizona Insurance Services Vulnerable - High Risk F Independent insurance agency; technical baseline gap observed: missing DMARC record and SPF soft-fail (~all), posing business email spoofing risk for policyholders.
30fold Benefits Arizona Legal & Identity Protection Vulnerable - High Risk F Legal and identity protection employee benefits advisory; technical baseline gap observed: missing SPF and DMARC records on primary domain.
The Goodman Taylor Team Ahwatukee / Phoenix, AZ Residential Real Estate Vulnerable - High Risk F East Valley residential real estate team; email authentication in monitor-only mode (p=none) with placeholder reporting address.
Kyrene Rotary Club Ahwatukee, AZ Civic & Community Service Vulnerable - High Risk F Active local civic service organization; technical baseline gap observed: missing DMARC record on primary organizational domain.
Community Action Security Arizona Security Patrol & Guard Services Vulnerable - High Risk F Physical security patrol and guard provider; technical baseline gap observed: missing DMARC record on primary domain.
Caring Transitions of Central AZ Arizona Senior Relocation & Estate Sales Vulnerable - High Risk F Senior relocation and estate management provider; technical baseline gap observed: missing SPF and DMARC records on primary domain.
Satya Yoga Center Phoenix, AZ Health & Yoga Studio Vulnerable - High Risk F Certified Iyengar yoga center; email authentication in monitor-only mode (p=none) with DMARC policy not actively enforcing unauthorized senders.
Advocate Planning Principles, Inc. Phoenix, AZ Financial Planning / Insurance Vulnerable - High Risk Not Scored Passive email-authentication baseline failure observed in September 2026: no SPF or DMARC record was returned for the primary domain. Public Arizona business records identify Advocate Planning Principles, Inc. as an active Phoenix finance and insurance corporation. This is not evidence of compromise.
OPACS Arizona Office Products / Business Services Vulnerable - High Risk Not Scored Domain has Google MX and SPF, but DMARC is only p=none and does not enforce protection against unauthorized sending. Public company information identifies OPACS as a locally owned office-products and business-services company developed by Travis and Donna Kimmel. This is not evidence of compromise.
BIO-ELITE Training Systems, LLC Scottsdale, AZ Wellness / Fitness Services Vulnerable - High Risk Not Scored Passive email-authentication baseline issue: SPF was not returned, and DNS exposed conflicting DMARC policy strings rather than one clean, authoritative record. Public site identifies BIO-ELITE Training Systems, LLC as a Scottsdale fitness and executive-health provider; Arizona business records identify Gianni Del Franco with the entity. This is not evidence of compromise.
Gryath Glass Laveen / Phoenix, AZ Automotive / Mobile Auto Glass Vulnerable - High Risk Not Scored Passive email-authentication baseline failure: no SPF or DMARC record was returned. Public site and Arizona Hispanic Chamber listing identify Gryath Glass as a Laveen-based mobile auto-glass, repair, and calibration provider. This is not evidence of compromise.
Hana Entertainment Phoenix / Mesa, AZ Events / Entertainment Vulnerable - High Risk Not Scored Domain has active Google MX and SPF, but DMARC is only p=none. The tested apex returned HTTP 404 while public event listings and Hana pages identify an Arizona event-production and entertainment business. This is not evidence of compromise.
Gryphon Roofing & Construction Tempe / Phoenix metro, AZ Construction / Roofing Vulnerable - High Risk Not Scored Domain has Google MX and SPF, but no DMARC record was returned. Public company pages identify Gryphon Companies, Inc. as an Arizona roofing, remodeling, and restoration provider operating since 1994. This is not evidence of compromise.
Handyman Connection of Phoenix Phoenix, AZ Home Services / General Contracting Vulnerable - High Risk Not Scored Domain has Microsoft 365 MX and SPF, but DMARC is only p=none. Public location pages identify the Phoenix operation, Allen Hopkins, the Northern Avenue address, and Arizona contractor license numbers. This is not evidence of compromise.
Happy Bees Pest Control / Arcadia Pest Management Arizona Pest Control Vulnerable - High Risk Not Scored Listed domain has active mail routing and SPF, but DMARC is only p=none. The site redirects to Arcadia Pest Management, and public business results identify Arcadia as formerly Happy Bees Pest Control. This is not evidence of compromise.
Back to Motion Chiropractic / Dr. Jennifer Polk Scottsdale, AZ Healthcare / Chiropractic Vulnerable - High Risk Not Scored Listed domain has active registrar-hosted mail, but no SPF or DMARC record was returned. The domain redirects to Dr. Jen Polk’s site; public pages identify Back to Motion Chiropractic in Scottsdale and Dr. Jennifer Polk as a licensed chiropractic physician. This is not evidence of compromise.
The Causey Effect / Bare Aesthetics Scottsdale, AZ Aesthetics / Nutrition / Wellness Vulnerable - High Risk Not Scored Listed domain has active Google MX, but no SPF or DMARC record was returned. Public records identify The Causey Effect, LLC and connect Christalyne Causey with the Scottsdale practice; the domain currently redirects to Bare Aesthetics. This is not evidence of compromise.
US Cleaning Solutions Peoria / Phoenix metro, AZ Commercial Cleaning Vulnerable - High Risk Not Scored Domain has active mail routing and SPF, but no DMARC record was returned. Public site and business directories identify US Cleaning Solutions as a commercial-cleaning provider serving Scottsdale, Phoenix, Glendale, and the greater metro, with a Peoria address. This is not evidence of compromise.
Western Alliance Bank Phoenix / Nationwide Banking / Financial Services Vulnerable - High Risk Not Scored Listed domain has Proofpoint MX and SPF, but DMARC is only p=none. The listed domain redirects to Western Alliance Bancorporation’s public site, which identifies Western Alliance Bank as a national commercial bank headquartered in Phoenix. This is not evidence of compromise.
One Handsome Bastard Distillery Scottsdale, AZ Distillery / Hospitality Vulnerable - High Risk Not Scored Domain has Microsoft 365 MX and SPF, but DMARC is only p=none. Public site and local reporting identify One Handsome Bastard as a Scottsdale micro-distillery and grill at 7042 E Indian School Road, operated by the Ritchie family. This is not evidence of compromise.
Window Coverings By Julie Carefree / Scottsdale, AZ Interior Services / Window Coverings Vulnerable - High Risk Not Scored Domain has active Google MX and SPF, but DMARC is only p=none. Public site and Scottsdale Chamber information identify the Carefree/Scottsdale window-coverings business, Julie Clark, and its showroom address. This is not evidence of compromise.
Golden Development Group (goldendevelopmentgroup.com) Chicago, IL / National Real Estate Acquisition Vulnerable - High Risk Not Scored Unsolicited off-market property solicitation pointing to a domain registered 2026-07-30 (roughly two months old). The site brands itself "Golden Retreat - The Private Alternative to Listing" and describes itself as doing business as Golden Development Group, while the solicitation used the name "Golden Development" - the domain name does not match the brand it presents. No named principal, no real estate license number, no physical address, and the only published contact is a personal Gmail address. The domain name overlaps an unrelated, established firm at goldendevgroup.com. Passive technical note: no MX, no SPF, no DMARC and no DKIM - the domain cannot send or receive authenticated mail; DNS is hosted on NS1/Netlify and both A records resolve to AWS eu-central-1 (Frankfurt, DE).

Vulnerable listings require evidence-based risk indicators. Non-response may strengthen the case for public listing, but the only public negative category is Vulnerable and each listing should carry a specific documented reason.

Remediation and Removal Policy

Businesses may request review after a listed issue has been remediated. When credible remediation evidence is provided, the listing may be updated to reflect that change. However, remediation alone does not automatically remove a business from public tracking.

If the originally observed issue is no longer present, the business will typically move out of the Vulnerable category and into Verified only after full validation against the published baseline. This is intentional: removal from the status board requires affirmative evidence that the broader security baseline is being met.

Need a listing reviewed after remediation? Submit for verification or open a support request via chat and include the business name, domain, the issue addressed, and supporting evidence.

πŸ“Š Weekly Cyber Threat Brief

Week of September 28 – October 4, 2026 β€” Actively exploited NetScaler and FortiMail zero-days, Apple CoreGraphics zero-day, Warlock SharePoint ransomware, and Arizona courts 1.3M FARE breach.

Current live brief. Older weeks are archived below.

🚨 This Week's Readout

  • Citrix NetScaler exploited zero-day duo (CVE-2026-88771 & CVE-2026-88772, CVSS 9.5) + SAML DoS (CVE-2026-88779, CVSS 8.7) β€” Vendor-confirmed in-the-wild zero-days allowing unauthenticated remote code execution on default configs and DTLS VPN servers. Attackers are actively planting webshells and persistent backdoors; firmware upgrades alone do NOT disinfect compromised appliances. Thorough compromise assessment is mandatory.
  • Fortinet FortiMail path traversal (CVE-2026-104286, CVSS 9.8) β€” Added to CISA KEV on Oct 1 under active exploitation. Unauthenticated HTTP/HTTPS requests permit arbitrary file writes. Official patches were pending upon disclosure; operators must immediately disable Identity-Based Encryption (IBE) support or isolate management interfaces per advisory FG-IR-26-175.
  • Apple CoreGraphics arbitrary code execution (CVE-2026-86950) β€” Targeted exploitation observed against high-risk individuals via crafted media files. A public proof-of-concept emerged Oct 1, accelerating the risk across all environments. Expedite patches for iOS/iPadOS 26.7.1, macOS Tahoe 26.7.1, and macOS Sequoia 15.8.1.
  • Warlock SharePoint ransomware campaign β€” Longlegs / Storm-2603 expanded attacks against critical infrastructure (water, telecom, regional gov). Operators stole ASP.NET machine keys, disabled security tools across 40+ systems using BYOVD vulnerable drivers, tunneled through VS Code, and staged ransomware in domain SYSVOL shares.
  • Southwestern Priority: Arizona court system breach β€” Sept 30 disclosures confirmed unauthorized extraction of 3 datasets from compressed backup servers, including the statewide FARE Collection Program database with ~1.3 million citizens' names, case numbers, and SSNs dating back 30 years, alongside sensitive protective orders. No court operational shutdown occurred.
πŸ”₯
9.8 / 9.5
Active Zero-Days: FortiMail & NetScaler
βš–οΈ
1.3M
AZ Courts FARE Debt Records Exposed
πŸ›‘
230
Weekly Ransomware Disclosures (82 US)
πŸͺ–
3.05M
Pentagon / DMDC Historical Exposure
πŸ›‘ Critical Zero-Days & Exploited Vulnerabilities
  • Citrix NetScaler (CVE-2026-88771 & CVE-2026-88772, CVSS 9.5) β€” Actively exploited zero-days allowing unauthenticated command execution and RCE/DoS via DTLS VPN virtual servers. Palo Alto Unit 42 confirmed webshell deployment in the wild. A firmware patch alone does not clean an infected appliance; thorough compromise assessment is mandatory.
  • Citrix NetScaler SAML Flaw (CVE-2026-88779, CVSS 8.7) β€” Memory-overflow denial of service flaw when operating as SAML SP or IdP. This is distinct from the RCE flaws, meaning initial patches do not cover every newly exploited angle.
  • Fortinet FortiMail Path Traversal (CVE-2026-104286, CVSS 9.8) β€” Unauthenticated arbitrary file write via HTTP/HTTPS added to CISA KEV on Oct 1 (federal remediation deadline Oct 4). Fixes were pending; disable IBE or cut public management access immediately.
  • Apple CoreGraphics (CVE-2026-86950) β€” Fixed Sept 28 in iOS/iPadOS 26.7.1, macOS Tahoe 26.7.1, and macOS Sequoia 15.8.1. Maliciously crafted files execute code. Targeted attacks confirmed; public PoC released Oct 1.
  • GitLab AI Gateway Sandbox Escape (CVE-2026-90970, CVSS 9.9) β€” Authenticated Duo Agent Platform prompt-template sandbox escape allowing command execution on self-hosted gateways. Fixed in 19.2.4, 19.3.2, and 19.4.1.
  • TeamViewer High-Severity Maintenance β€” Five vulnerabilities patched (including remote-session access controls); no active public exploitation confirmed, keep in routine patch queue.
πŸ”“ Major Data Breaches & Leaks
  • Arizona Judicial Branch / FARE Program (~1.3M) β€” Disclosed Sept 28 with Sept 30 update: threat actors copied three datasets from a compressed backup server. The FARE dataset contains ~1.3 million individuals with 30-year court debt histories, case numbers, and SSNs. Additional copied records include active and expired protective orders, introducing physical safety risks.
  • Pentagon / Defense Manpower Data Center (~3.05M) β€” Historical breach confirmed Sept 28–29 affecting 2.76 million living and 294,000 deceased military personnel. Caused by a file-sharing flaw exploited between Oct 2025 and July 2026 (patched July 16), exposing SSNs, birth dates, and service details.
  • Technical University of Denmark (DTU) (~200,000) β€” Compromised credentials in the DTUBasen identity system led to massive data extraction of national IDs, addresses, employment records, and next-of-kin information.
  • Tokyo Metro (59,000) β€” Email address exposure of 59,000 members confirmed and remediated; no train operational impact.
  • PixelLeak Developer Exposure β€” Research revealed over 13,000 internal screenshots from 300+ organizations leaked across 900+ public personal GitHub repos, exposing corporate credentials, API keys, and internal customer dashboards.
🦠 Ransomware, Cloud Sabotage & Disruptions
  • Warlock (Storm-2603 / Longlegs) Critical Infrastructure Campaign β€” New research revealed intrusions against water utilities, telecom, and regional government entities. Attackers leveraged SharePoint vulnerabilities, stole ASP.NET machine keys, utilized vulnerable BYOVD drivers to kill EDR agents across 40 systems, established VS Code tunnels, and staged ransomware payloads directly in domain SYSVOL shares.
  • JadePuffer (Storm-3168) Destructive Azure Operations β€” Microsoft documented an 18-hour destructive cloud attack where threat actors abused compromised service principals to permanently delete Azure Storage, SQL databases, Key Vaults, App Services, VMs, and recovery-protection locksβ€”targeting cloud non-human identities directly.
  • Operation Killswitch: KillSec Leak Site Seized β€” Law enforcement seized KillSec's leak site infrastructure, arresting three suspects (including a 16-year-old admin) and securing 110+ terabytes of exfiltrated victim data.
  • Keio Corporation (Japan) Ransomware β€” Ransomware crippled payment and hotel booking systems at the Keio Plaza Hotel Tokyo; train operations remained unaffected.
  • Ransomware.live Weekly Watch (230 Disclosures) β€” Settra claimed Holly Poultry (435 GB), The Gentlemen claimed Aware, Inc. (400 GB) and Center State Engineering (340 GB), and Booba Project claimed MorseLife Health System (344 GB).
🌡 Southwestern US Signal & Emerging Operator Threats
  • Arizona Courts Breach Deep-Dive β€” Officials confirmed the intrusion originated from an employee clicking a malicious search result mimicking a legitimate link. The data originated from compressed backups, and as of Sept 30, no evidence exists that data has been traded or decrypted online. No ransom demand was issued and no court shutdown occurred. MSPs should warn clients of incoming phishing and debt collection scams impersonating court clerks.
  • EdgeEndo USA (Albuquerque, NM) β€” Dental technology manufacturer listed on Booba Project's leak site on Oct 2 claiming 103 GB stolen; no operational closure or disruption verified.
  • Huntress ClickFix via Custom GPTs β€” Over 40 corporate intrusions traced to malicious Google Sites and weaponized Custom GPTs using fake CAPTCHAs to fool users into pasting PowerShell droppers that deploy remote-access malware.

Week of September 28 – October 4, 2026. Information cutoff: October 5, 2026. Older reports archived below. Sources: Citrix Support, SC Media, NVD, Help Net Security, SecurityWeek, Palo Alto Unit 42, KVOA News 4, Ransomware.live.

πŸ“š Threat Brief Archives

Previous weekly threat intelligence reports

πŸ“Š September 14–21, 2026

The week was dominated by two actively exploited Cisco zero-days in Secure Email Gateway (CVE-2026-76461 root RCE) and Cisco ISE (CVE-2026-76460 auth bypass), three Linux kernel vulnerabilities added to CISA KEV, a record-shattering 997 ransomware attacks in August, ShinyHunters hijacking Cl0p's leak site, and a 23.6M-record Gyazo breach.

πŸ›‘ Zero-Days & Patches

  • Cisco Secure Email Gateway (CVE-2026-76461, CVSS 9.8) β€” Unauthenticated SQL injection yielding root command execution via inbound mail flow.
  • Cisco ISE (CVE-2026-76460, CVSS 10.0) β€” Pre-disclosure exploited API vulnerability granting complete appliance takeover.
  • Linux Kernel Trio β€” CVE-2025-39682, CVE-2026-53266, and CVE-2025-39964 added to CISA KEV.

πŸ”“ Breaches & Intrusions

  • Gyazo (Helpfeel) β€” 23.62M user accounts stolen via image upload server exploit.
  • CenterPoint Energy (Houston) β€” 7.5M utility customer records leaked on dark web.
  • IDScan.net β€” Vendor confirmed breach after 153M driver's license scans listed for sale.

🦠 Ransomware & Turf Wars

  • ShinyHunters vs. Cl0p β€” Cl0p's Tor leak site hijacked via Grav CMS file-upload flaw.
  • August Attack Record β€” 997 attacks (+23%), manufacturing hit hardest with 22% of victim volume.
  • Settra Ransomware β€” 93 victims claimed, abusing MeshAgent RMM and BYOVD evasion.
πŸ“Š September 7–14, 2026

Microsoft's September Patch Tuesday delivered a record 964–974 CVEs including two actively exploited zero-days in the Windows Update Stack (CVE-2026-81963) and Windows ALPC (CVE-2026-85880), alongside 20 wormable unauthenticated RCEs in DNS Server (CVE-2026-69730) and Remote Desktop Services (CVE-2026-69525). Veradigm disclosed a 3.5M patient record breach, Mathspace suffered 1M student/parent records leaked via Metabase SQLi, and Specialty Textile Services in Phoenix was hit by incRansom.

πŸ›‘ Zero-Days & Patches

  • Windows Update Stack (CVE-2026-81963) β€” First Update Stack zero-day on record; improper link resolution before file access enabling local EoP to SYSTEM.
  • Windows ALPC (CVE-2026-85880) β€” Heap overflow / out-of-bounds write enabling sandbox escape from low-priv AppContainer to SYSTEM with zero user interaction.
  • Wormable RCEs β€” Windows DNS Server (CVE-2026-69730) and Remote Desktop Services (CVE-2026-69525), both CVSS 9.8.

πŸ”“ Breaches & Intrusions

  • Veradigm (~3.5M) β€” Healthcare patient data breach via vendor credential compromise.
  • Mathspace AU/NZ (~1.08M) β€” Metabase CVSS 10 SQLi exploited by ShinyHunters.
  • Specialty Textile Services (Phoenix, AZ) β€” Local hospitality linen provider listed on incRansom leak site.
πŸ“Š August 24, 2026

Active hypervisor exploitation dominated the week with VMware vCenter (CVE-2026-59310) abused for Babuk ransomware deployment, SAP Commerce Cloud under CVSS 10.0 attacks, and WordPress Forminator (CVE-2026-15748) threatening 600k+ sites. Major regional disruption hit Texas with UT San Antonio class delays and JPS Health Network in Fort Worth operating under manual clinical downtime.

πŸ›‘ Zero-Days & Patches

  • VMware vCenter (CVE-2026-59310) β€” Actively exploited in the wild for remote code execution and deployment of Babuk-derived ransomware directly into virtualized server clusters.
  • SAP Commerce Cloud (CVE-2026-58231, CVSS 10.0) β€” Perfect 10.0 critical issue under active exploitation against enterprise commerce infrastructure.
  • WordPress Forminator Forms (CVE-2026-15748) β€” Affecting 600,000+ active installs allowing unauthenticated arbitrary file uploads and potential server takeover.

πŸ”“ Breaches & Intrusions

  • The Butcher Brothers (Play Ransomware) β€” Corporate data exfiltrated and operational shutdown following Play ransomware listing.
  • France Finance Ministry (~700,000) β€” Confirmed theft of taxpayer data affecting roughly 700,000 citizens.
  • Bits of Gold (~200,000) β€” Third-party vendor breach affecting approximately 200,000 cryptocurrency customers.

🦠 Ransomware & Healthcare Disruption

  • AnMed (South Carolina) β€” Severe ransomware attack forced broad facility closures and operational delays.
  • UT San Antonio & JPS Health Network (Texas) β€” Fall classes delayed following breach containment; Fort Worth health system forced into multi-day manual downtime with EHR offline.
  • Fort Smith City Systems β€” Municipal network security incident disrupted city services.
πŸ“Š July 11-18, 2026

Microsoft's July Patch Tuesday fixed 570 flaws including 2 actively exploited zero-days in AD FS (CVE-2026-56155) and SharePoint (CVE-2026-56164). AssuranceAmerica (~7M), Medtronic (>3.8M), and Moody Bible Institute (>2.3M) disclosed major breaches, while JadePuffer demonstrated the first documented fully agentic LLM-driven ransomware flow.

πŸ“Š June 25, 2026

The defining stories were brutal small-business breach reality (43–47% targeted breach rate for orgs with ≤10 users, 60% closing within six months), relentless ransomware leak-site activity across Southwest sectors, and cascading infrastructure outages (Cloudflare, BeyondTrust).

πŸ›‘ Zero-Days & Patches

  • Microsoft addressed 128–137 vulnerabilities including one zero-day (CVE-2025-49719) in SQL Server.
  • SPNEGO NEGOEX RCE (CVE-2025-47981) β€” wormable CVSS 9.8 affecting Windows Server 2016–2025 and Windows 10 with PKU2U.
  • KDC Proxy Service RCE (CVE-2025-49735) β€” critical RCE in KPSSVC on Windows Server 2016–2025.

πŸ”“ Breaches & Intrusions

  • Ransomware leak sites β€” Qilin and Akira highly active; Shipping Association of NY and NJ listed.
  • June 7–8 leaks β€” Plaza Lama and Hansoll Textile (Vietnam) among claims.
  • BeyondTrust β€” active exploitation of a critical appliance vulnerability observed.

🦠 Ransomware

  • 88% of SMB breaches involve ransomware (vs. 39% for larger enterprises).
  • Southwest targets: Nunez Dental, Mount Rogers Community Services, Jericho FD, Sandhills Medical, M&H Electric, Triumph Construction.
  • Median demands $25K–$120K (sub-10 employees), up to $254K (sub-50 users), downtime up to 72 hours.
πŸ“Š May 19, 2026

The defining story of the week was the Instructure/Canvas SaaS breach and extortion pressure affecting schools nationwide, including Southwest institutions, alongside an exploited LNK coercion chain and new KEV additions.

πŸ›‘ Zero-Days & Patches

  • Microsoft Windows LNK chain β€” Zero-click authentication coercion via malformed shortcut files patched.
  • CISA KEV additions β€” Actively exploited flaws in SimpleHelp, Samsung MagicINFO 9, and D-Link routers.
  • Chrome zero-day β€” Actively exploited Chrome zero-day patched.

πŸ”“ Breaches & Intrusions

  • Instructure / Canvas β€” Names, email addresses, student IDs, and messages exposed.
  • Southwest US β€” Anthony, NM municipal incident (missing records/systems) and Nevada school system fallout.
  • Jones Day β€” Silent ransomware posted stolen data from the law firm.
πŸ“Š April 16–23, 2026

Patch-heavy week dominated by Microsoft April Patch Tuesday follow-through, Adobe Acrobat Reader emergency patching, Fortinet EMS exposure, SAP NetWeaver exploitation, and third-party access claims.

πŸ›‘ Zero-Days & Patches

  • Microsoft fixed two exploited zero-days: CVE-2026-32201 and CVE-2026-33825.
  • Adobe Acrobat Reader CVE-2026-34621 and Fortinet FortiClient EMS CVE-2026-21643 remained urgent patch items.
  • SAP NetWeaver CVE-2025-31324 was tied to web-shell uploads on exposed systems.

πŸ”“ Breaches & Intrusions

  • OneDigital, CareCloud, Erie Family Health, and Rockstar/Anodot/Snowflake-related claims were tracked as notable disclosure items.
  • ShinyHunters, The Gentlemen, Medusa/Storm-1175, Interlock, and Qilin remained notable ransomware or intrusion-trend names.
πŸ“Š April 10–17, 2026

🚨 Patch These NOW

  • Chrome/Edge β€” CVE-2026-5281 (zero-day, actively exploited). Update to 146.0.7680.177+.
  • F5 BIG-IP β€” CVE-2025-53521 (CVSS 9.8 RCE), 14,000+ exposed.
  • Fortinet EMS β€” CVE-2026-35616 and CVE-2026-21643 (pre-auth RCE).

πŸ›‘ Zero-Days & Patches

  • CVE-2026-32201 β€” SharePoint spoofing zero-day, actively exploited.
  • CVE-2026-5281 β€” Chrome Dawn/WebGPU use-after-free zero-day.
  • Eight critical Office/Word RCE bugs (up to CVSS 8.4).
  • Firefox 149.0.2 and Thunderbird 149.0.2 also required patching.

🦠 Ransomware

  • 21-35 new victims were appearing daily in early April reporting.
  • LockBit and SafePay were among the most active groups tracked that week.
  • Qilin, Akira, and DragonForce accounted for a large share of observed activity.
  • LeakBase seized β€” 142,000+ user cybercrime forum shut down.
πŸ“Š April 7–14, 2026

πŸͺ Small Business Breaches

59 breaches exposing 97.7 million records in 2026 alone. Average ransom demand: $84,000

  • Hennessy Advisors β€” 12,643 individuals (SSNs, financial accounts, driver's licenses)
  • North Central Behavioral Health Systems β€” Patient PHI exposed
  • Evergreen Healthcare Group β€” SSNs, medical info, DOBs exposed

πŸ”“ Major Breaches

  • TriZetto Provider Solutions (Cognizant) β€” 3.4M individuals
  • LexisNexis Risk Solutions β€” ~2GB internal data leaked
  • FBI Surveillance/Wiretap Systems β€” Confirmed investigation

πŸ›‘ Critical Zero-Days

  • Chrome CVE-2026-5281 β€” 4th zero-day of 2026, Use-After-Free in Dawn (WebGPU), actively exploited. Update to 146.0.7680.177+
  • F5 BIG-IP CVE-2025-53521 β€” 14,000+ exposed, CVSS 9.8 RCE
  • Fortinet FortiClient EMS β€” CVE-2026-35616, CVE-2026-21643 (pre-auth RCE)
  • Axios npm β€” Supply chain attack, versions 1.14.1 and 0.30.4 backdoored

🦠 Ransomware

  • Anubis β€” Claimed 170GB theft
  • DragonForce β€” Hit Neurological Associates of Washington (1.4TB)
  • Rhysida β€” Hit Cheyenne & Arapaho Tribes, $680K demand
  • LeakBase seized β€” 142,000+ user cybercrime forum shut down
⚠️ Secure Boot Deadline

June 26, 2026 β€” 73 days out. Push UEFI updates now. April 14 and May 12 are your last clean Patch Tuesday windows.

More archives coming as weeks accumulate. Historical data helps track threat trends over time.

πŸ“Š April 2–9, 2026
  • F5 BIG-IP CVE-2025-53521 β€” 14,000+ exposed, CVSS 9.8 RCE actively exploited
  • Fortinet FortiClient EMS β€” CVE-2026-24858, CVE-2026-35616 under urgent patching
  • Akira, Timc, Anubis β€” 20+ new victims on leak sites, targeting healthcare, manufacturing, IT
  • Axios npm supply chain β€” Malicious packages 1.14.1/0.30.4 deployed backdoors
  • Cisco AWS keys β€” Stolen in breach, unauthorized cloud access
πŸ“Š March 26 – April 2, 2026
  • Langflow RCE CVE-2026-33017 β€” CISA KEV, exploited within 20 minutes of disclosure
  • Ransomware β€” 780 attacks in March (up 13%), Qilin (140) and Akira (80) most active
  • Supply chain β€” LiteLLM PyPI, Axios npm, TeamPCP targeting CI/CD
  • Breaches β€” Navia Benefit Solutions (2.7M PII), North Texas Behavioral Health (284K), OSI Systems (4.9K)
  • Outages β€” 325 global network outages (up 17%)
πŸ“Š March 19–26, 2026
  • March Patch Tuesday β€” 79-82 CVEs, critical RCE in Devices Pricing Program (CVE-2026-21536, CVSS 9.8)
  • Fortinet FortiWeb β€” CVE-2026-24017 auth bypass enables brute-force
  • Medusa ransomware β€” UMMC (1TB+ patient data, $800K), Passaic County NJ
  • Stryker attack β€” Iranian Handala group, 200K+ devices wiped, 50TB stolen
  • Ongoing exploits β€” SharePoint RCE, Cisco FMC zero-day, ConnectWise ScreenConnect
πŸ“Š March 5–12, 2026
  • Microsoft Patch Tuesday β€” 82 flaws, Excel zero-click info disclosure (CVE-2026-26144)
  • Android zero-day CVE-2026-21385 β€” Confirmed exploited, CISA added to KEV
  • LexisNexis breach β€” 3.9M records, AWS secrets, Salesforce creds exposed
  • ServiceNow outage β€” March 6, 63 mins, global customers impacted
πŸ“Š February 19–26, 2026
  • SolarWinds Serv-U β€” 4 critical RCE flaws (CVE-2025-40538-41, CVSS 9.1), update to 15.5.4
  • Dell RecoverPoint CVE-2026-22769 β€” CVSS 10.0, China-nexus exploitation since mid-2024
  • APT28 zero-day CVE-2026-21509 β€” Russian state actor, MS Office exploit
  • Conduent breach β€” 25M+ Americans, one of largest in US history
  • Qilin ransomware β€” 100+ victims/month, 56% surge after RansomHub collapse
  • Cloudflare outage β€” Feb 20, ~5 hours, BGP misconfiguration (not cyber attack)
πŸ“Š Arizona & Southwest Breaches
  • University of Phoenix β€” 3.5M records, Clop ransomware (CVE-2025-61882), largest AZ breach
  • Academic Urology & Urogynecology of Arizona β€” 73K patients, PHI exposed
  • Arizona Lighting Sales β€” Play ransomware, Feb 2026
  • Conduent β€” State payment processor, AZ residents impacted

πŸ”΄ Critical Vulnerabilities & Zero-Days

Current priority (week of Sept 7–14, 2026): apply the record September Patch Tuesday for the two exploited zero-days and the wormable DNS/RDS RCEs, update Chrome/Edge now, and close Adobe Commerce before it reaches a leak site.

πŸ”΄ Windows Update Stack

CVE-2026-81963

Exploited zero-day β†’ SYSTEM

πŸ”΄ Windows ALPC

CVE-2026-85880

Exploited zero-day β†’ SYSTEM

πŸ”΄ Windows DNS Server

CVE-2026-69730

CVSS 9.8 RCE (wormable)

πŸ”΄ Remote Desktop Services

CVE-2026-69525

CVSS 9.8 RCE β€” More Likely

🟠 Chrome / Edge (V8)

CVE-2026-85046

Exploited zero-day, patch now

🟠 Adobe Commerce/Magento

CVE-2026-75650

KEV β€” template engine
🟒 September 2026 Patch Tuesday β€” Records, Zero-Days & Action
  • Scale: Largest Patch Tuesday on record β€” roughly 964–974 Microsoft CVEs (104 Critical, 860+ Important). BleepingComputer / Tenable.
  • Two exploited zero-days (patch first): CVE-2026-81963 Windows Update Stack EoP and CVE-2026-85880 Windows ALPC EoP β€” both local privilege escalation to SYSTEM, both exploited in the wild. SecurityWeek.
  • Wormable RCEs (~20): Prioritize Windows DNS Server CVE-2026-69730 (CVSS 9.8, use-after-free, "Exploitation More Likely") and Remote Desktop Services CVE-2026-69525 (CVSS 9.8). Also fix Exchange Server CVE-2026-55007 (RCE), SharePoint CVE-2026-69465 (RCE), Authenticator EoP CVE-2026-80097, and SQL Server EoP CVE-2026-65669. Rapid7.
  • Browsers: Chrome/Edge V8 zero-day CVE-2026-85046 (patched around Sept 2–3) β€” update Chrome and Edge to the latest stable channel now; CISA added it to KEV. CISA.
  • Action this week: Apply the September cumulative updates across Windows Server 2016–2025 and Windows 10 via WSUS/Windows Update; deploy the servicing-stack updates for older builds; patch DNS/Exchange/SharePoint/RDS before anything else touches the perimeter; update Chrome/Edge; close Adobe Commerce/Magento (CVE-2026-75650, KEV); and verify backup/recovery isolation given the EoP-to-SYSTEM chains that precede ransomware.
πŸ”΄ Microsoft SharePoint CVE-2026-32201 β€” Exploited Spoofing Zero-Day

Microsoft's April 14 Patch Tuesday fixed this SharePoint Server spoofing zero-day, reported as exploited in the wild.

Action: Confirm April Microsoft patches are applied to SharePoint infrastructure and review exposed collaboration services.

πŸ”΄ Microsoft Defender CVE-2026-33825 β€” Privilege Escalation Zero-Day

Microsoft's April 14 Patch Tuesday also fixed a Defender elevation of privilege zero-day. The week of April 23–30 did not add another comparable Microsoft emergency.

Action: Verify endpoint patch compliance and prioritize systems with delayed Defender platform updates.

πŸ”΄ Vercel β€” Source Code and API Key Exposure

Vercel confirmed an April 17–23 breach involving 580 employee records, source code, and API keys.

Action: Rotate exposed credentials, review repository access, and check downstream services for suspicious API activity.

🟠 Kemper Corporation β€” ShinyHunters Data Theft Claim

ShinyHunters announced an April 15 Kemper Corporation data exposure claim totaling 29GB, including payment-related data.

Action: Treat payment exposure as the primary risk until formal notice details narrow the scope.

🟠 Ransomware Leak Sites β€” Low Week, High Q1 Baseline

Ransomware leak-site posts rose 22% in Q1 2026 to 2,638, driven by The Gentlemen gang with 179 posts. No new large leak-site breaches were confirmed during April 23–30.

Action: Keep backup restore tests and endpoint coverage active even during quieter reporting weeks.

πŸ› οΈ Other Notable β€” Closures, Southwest, and Outages
  • No full closures β€” No companies reported complete shutdowns from cyber incidents during April 23–30.
  • Southwest US β€” No additional Southwestern US breaches, closures, or attacks were reported.
  • Verizon Business β€” Phoenix and Chandler, AZ outage lasted 1 hour 3 minutes and is tracked as non-cyber.
  • Arizona audit β€” Material weaknesses were noted, but no active incident was reported.
πŸ”΄ Windows Message Queuing RCE Trio β€” Network Wormable

CVE-2025-53143/53144/53145 (CVSS 8.8) β€” Three separate type confusion bugs in Windows MSMQ. Network attackers can execute code remotely without authentication.

Why it matters: Wormable potential β€” this could spread like WannaCry. High clickbait value because "Windows Message Queuing" sounds obscure but affects core Windows networking.

Action: Apply April 2026 patches. Prioritize servers with MSMQ enabled.

πŸ”΄ HTTP/2 Rapid Reset β€” Highest Exploitation Probability

CVE-2023-44487 β€” EPSS Score: 0.94 (highest in the industry). Used in the largest-ever DDoS attacks (2023).

Why it matters: Near-certain exploitation probability. If you're running HTTP/2 servers, this is already being exploited against you.

Action: Patch CDN/WAF providers, ensure HTTP/2 rate limiting is configured.

🟠 NVIDIA Driver CVE-2021-1051/1052 β€” 5 Years Unpatched

CVE-2021-1051/1052 β€” NVIDIA driver from 2019 still sitting on endpoints in 2026. Driver updates fall outside standard patch cycles.

Why it matters: Perfect "your IT hygiene is showing" example. This CVE is 5+ years old and still active because GPU drivers never get patched. No client details needed to write this up.

Action: Audit NVIDIA driver versions. Push driver updates through your patch management or MDM.

πŸ› οΈ More Worth Watching β€” SMB, NTLM, Firefox
  • Windows SMB EoP β€” CVE-2025-55234 (CVSS 8.8). SMB bugs always get attention.
  • NTLM EoP β€” CVE-2025-53778 / CVE-2025-54918 (CVSS 8.8). NTLM is a perennial favorite.
  • Firefox Canvas2D β€” CVE-2025-10527/10528, CVE-2025-11152 (sandbox escapes). Relatable to everyday users β€” "your browser could be pwned."

🚨 Confirmed Breaches

Based on public records, government filings, and verified client notifications.

πŸ”΄ Veradigm β€” Patient Records (The Gentlemen Ransomware)

Healthcare-tech company disclosed a patient-data breach after a third-party vendor's credentials exposed a customer-services API. The Gentlemen gang claims 3.5M patient records (names, addresses, SSNs) and threatens a leak unless paid.

Disclosed: Week of Sept 8, 2026 | Source: BleepingComputer

🟠 Mathspace β€” 1.08M Student Records (ShinyHunters)

Online math platform (AU/NZ) disclosed a breach affecting 1,079,819 students, teachers, staff and parents after a self-hosted Metabase instance was hit via the CVSS-10 SQLi CVE-2026-72898. ShinyHunters claimed responsibility; the critical advisory was not escalated in time.

Disclosed: Sept 8, 2026 | Source: SecurityWeek

🟠 Specialty Textile Services (Phoenix, AZ) β€” incRansom

Phoenix-based linen/hospitality provider (~200–500 staff) hit by incRansom. Double-extortion attack discovered Sept 2, 2026; listed on the group's leak site. Local Phoenix signal for hospitality and supply-chain operators.

Discovered: Sept 2, 2026 | Source: Leak-site record (HookPhish / breach aggregators)

🟠 HYBE Weverse β€” 422K Accounts (Payment/Refund Data)

HYBE's superfan platform confirmed 422,584 accounts leaked, including payment and refund details. Reported to KISA after an external vulnerability disclosure. Second Weverse data incident this year.

Confirmed: Sept 6, 2026 | Source: Music Business Worldwide

🟑 Gangnam Unni (Healing Paper) β€” 219K Users

South Korea's leading cosmetic-procedure platform exposed 219,665 users' consultation records β€” including procedure/hospital names, appointment times, reasons for consultation and photos β€” through an API access breach.

Disclosed: Sept 8, 2026 | Source: Korea Herald

">
πŸ”΄ University of Phoenix β€” 3.5M Records (Clop Ransomware)

Clop exploited CVE-2025-61882 in Oracle E-Business Suite. Names, SSNs, birth dates, bank account/routing numbers for 3.49 million students/staff. Undetected for 3 months.

Disclosed: November 2025 | Largest AZ breach on record.

πŸ”΄ Conduent β€” 25M+ Americans (State Payment Processor)

Safepay ransomware. 8TB exfiltrated over 5 months (Oct 2024–Jan 2025). SSNs, health data, Medicaid/benefit info for 25M+ Americans. Notifications sent 9 months later.

Impact: Multiple states' government payment services.

πŸ”΄ Academic Urology & Urogynecology of Arizona β€” 73K Patients

Unauthorized intrusion May 18-22, 2025. Exposed: names, SSNs, tax IDs, driver's licenses, DOBs, financial details, health insurance, medical records.

Disclosed: January 30, 2026 | HIPAA-reportable.

🟠 Double D Taxes β€” IRS Data Exfiltration

Social engineering leading to credential leak. IRS and tax data exfiltrated via dark web leak.

Date: November 2025 | Source: Dark Web Leak

🟠 Arizona Lighting Sales β€” Play Ransomware

Play ransomware claimed Phoenix-area commercial lighting distributor. Double-extortion playbook. Data scope undisclosed.

Date: February 19, 2026

🟠 TriZetto Provider Solutions β€” 3.4M Health Records

Cognizant subsidiary. Health insurance and patient payment data compromised for 3.4 million individuals.

Type: Healthcare payment platform breach.

🟠 Phoenix Art Museum β€” Breach Disclosed April 15

Cybersecurity incident confirmed. Number of records exposed undisclosed.

🟠 Primary Health / U.S. HealthWorks (AZ) β€” 78K Records

Cyberattack / data theft. Names, DOB, SSNs exposed.

Date: January 2025 | Source: HHS OCR Breach Portal

🟑 Glendale Obstetrics & Gynecology β€” 500+ Patients

Network hacking incident. Patient records exposed.

Date: December 2025 | Source: HHS OCR Breach Portal

🟑 PayPal Working Capital β€” Configuration Error

Software coding error (not a hack). 5.5 months of exposed data: names, emails, phones, SSNs, DOBs. No network intrusion.

Date: Jul 1 – Dec 13, 2025 | Source: Public Disclosure

🟠 Stryker β€” Iranian Device-Wipe Attack (Tens of Thousands of Endpoints)

Iranian government hackers broke into medical tech giant Stryker in March 2026 and remotely wiped tens of thousands of employee devices. The attack caused widespread operational disruption and had a material impact on Stryker's first-quarter earnings. U.S. government attributed the hacking group to an arm of Iranian intelligence, marking a shift from espionage to destructive attacks.

Date: March 2026 | Source: TechCrunch / U.S. Government Attribution

πŸ”΄ Klue / Icarus β€” 200 Companies Exposed (Jamf, HackerOne, LastPass)

Market research provider Klue breached by Icarus extortion gang using a credential issued in 2022 that was never decommissioned β€” roughly 4 years of neglect. Hackers stole cloud service keys allowing access to Klue's customers' data stores, affecting close to 200 companies including cybersecurity giants Jamf, HackerOne, and LastPass. Klue reportedly paid ransom to prevent publication.

Date: 2026 | Source: TechCrunch / Verified Customer Notifications

πŸ”΄ Instructure / Canvas β€” 30M+ Students (ShinyHunters Double Breach)

ShinyHunters breached education tech giant Instructure's Canvas LMS, stealing private data of over 30 million students and staff. When Instructure didn't pay, hackers broke in again during finals week and defaced login screens across U.S. schools, disrupting exams nationwide. Instructure eventually paid ransom despite FBI discouragement. ShinyHunters also hit Charter (40M records via voice phishing) and Carnival Cruise (6M customer records).

Date: 2026 | Source: TechCrunch / FBI

πŸ“‹ Banner Health β€” Historical Reference (3.7M Patients)

Largest healthcare breach in AZ history. Settlement and public records.

Source: HHS Public Settlement Records

Have information about a local breach? Report it confidentially